Categories
Hosting Security

2026 PHP2SHELL…

So its 3am, and we’re up patching servers. Sigh…

Why?

https://www.php.net/archive/2026.php#2026-10-21-5

“What the heck?”, “What is that?” I hear you say…

Heres the run-down:
72% of the worlds public facing internet uses the coding language PHP in some way shape or form under the hood. Whether the site runs wordpress, or joomla, or lots of other content management systems, chances are pretty high it runs on top of PHP. Normally bugs and vulnerabilities are found in the code of these tools that are used on top of PHP. Today, by emergency declaration, PHP – the base level language that these tools run on, has published a bug that requires urgent patching by system administrators. Impacted systems could be exploited to gain behind the scenes access to the server, and compromise it further. Cloudflare – a worldwide CDN has published that they first saw exploits of the bug 7 hours before the official patch was released…

This is a big deal. Think of it like Cadbury’s issuing a food recall notice on ALL of their chocolate that has been sold in the last 8+ years. You’ll have to go back to the shop and get the antidote for the chocolate flaw as fast as you can, and until you do, ideally no chocolate for you. Oh – and your baked goods with chocolate in them? Yeah – sorry… Without the antidote, we can’t say if you’ll get sick or not, but if you do, it’ll be a 9/10 bad…
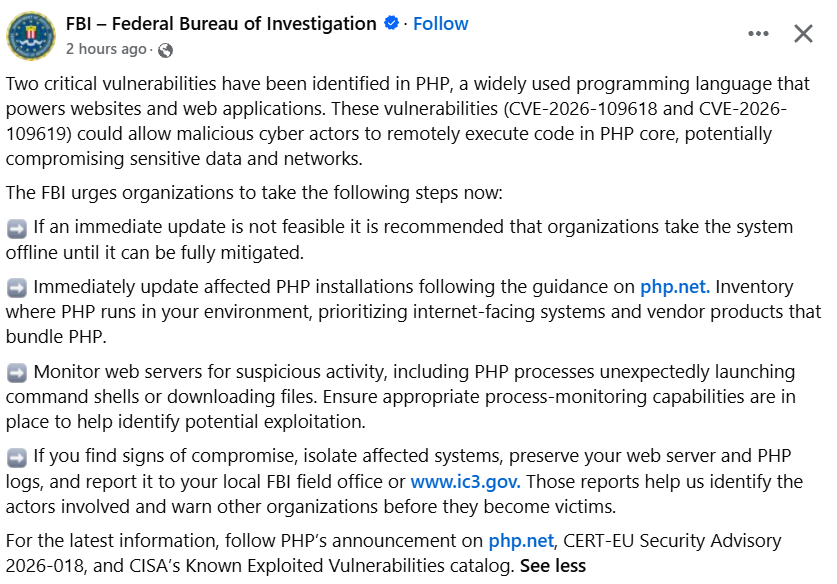
Yay for people using AI, finding the bug, and making the world a safer place. Boo to people using AI to build exploits soo darn fast now that as soon as something is known to have a flaw, chances are there is someone actively exploiting it to try to undermine legitimate internet websites.

Because this is a flaw in the underlying fabric of soo much of the internet, we are right now seeing thousands of websites down while patches are put in place, or from people trying to take advantage of this. Whats worse? That includes the websites that people are trying to get those patches from! For example, we have a server that runs Ubuntu operating system, and the version of PHP on there requires installation from https://ppa.launchpadcontent.net/ – a major provider of versions of php. But that site is returning 503 status errors, and is effectively down – likely due to too many requests for its content – people hoping that the version of php they need updated has been released.

Some providers are handling this better than others. cPanel, a major website hosting tools provider, released patched versions of PHP compatible with their systems fairly fast, and forced them out to all servers running their software within an hour of the official patched versions becoming available. Why this is good, is that covers many small business websites which are hsoted on shared hosting (more than one businesses website per server, helping to lower the costs of having a website available to the public) without people needing to think about it. Other website infrastructure teams will have real issues as servers and software tools will need entirely rebuilt in order to cater for the updated code. That can be months worth of work (although we’d hope that web systems haven’t been left to get to that sort of state by their maintainers/investors!).

We will see more of these in the future. As AI is increasingly used in the security space, to find problems before malicious actors do, we will get all sorts of weird and wonderful exploits being published, and because computers can do things soo quickly now-a-days, people will need to increasingly act faster to patch and protect infrastructure. Which sucks for those who’s job it is to make that happen lol. Increasingly cyber security has moved to being a 24/7 monitored requirement, no longer can you suffice with a quick audit and fix what is found when you can prioritise it.

Need help ensuring your online assets are safe? I know some people who can help
Categories
Community Development

Bragging

Something that has been grinding my gears recently is web agencies posting in their advertising how many websites they have made. Kudos to you on building some websites. What those figures don’t tell you is how happy the customer was with the work, what sized project they were, and where those customers are now.

There is a big difference between a 3-5 hour single page brochure website thrown together using existing templates so it looks the same as many other websites out there, as opposed to a large e-commerce, corporate intraweb or business processes site with hundreds of moving parts. Or from a blank canvas for the client to fill in content, to a well copywritten and targetted, designed and optimised website built to last.

Our job as web developers isn’t actually about selling code. Yes that is part of it, and we take pride in a job well done. But actually, we sell human interaction. Service. Was the process of getting to the destination with your software or website enjoyable, did we cover all the requirements and add value to your ideas, amplifying them, helping your business thrive. And do you feel good at the end of it. Have you got the support you need to take things to the next level?

So whilst you may see ads around, boasting thousands of websites delivered, trust people more than you trust billboards. Word of mouth, and results, speak far stronger than digits plastered about.

Categories
Hosting

Website Hosting – So what am I paying for?

You’ve got yourself a website, you’ve forked out money to get it built (or built it yourself – go you!) and then you get told that you’ll be paying an ongoing hosting fee for that website. This is where things get interesting as to what that includes, as it can leave you with surprises down the track if you go for the cheapest hosting option available to you, or if you find out later that you are getting over-charged. So we thought we’d break down what we do at Webmad, so you can see where your hard earned money is being spent.

The first part of website hosting is, you’ve got to have a server to host the website. Out on the internet, all websites are hosted somewhere – there will be one, or many, computers, powered on 24/7, waiting to respond with the right content at the right time, at your audiences request. If the server that serves your website isn’t on, your website won’t respond when requested, and your website will appear down. Not a great look.

But not all website hosting servers are made and configured equal. In order to maximise their revenue, some hosts cram as many websites as they can onto a single server. This is the same as running hundreds of applications on your home computer – they all just end up going slowly, if they respond at all. The more the websites on that server are under high demand, the slower all the sites on the server are going to perform. There are tools like Cloudlinux which can minimise the impact of this on a server, but in general, the more sites on a shared hosting server, the worse the performance of your site will be, even if the servers are massive.

Another way of maximising revenue is to use older or lower spec server hardware, or extend the usage life of existing hardware – the less you have to spend to replace hardware, the more revenue you make. While this can work, especially if the host is really only babysitting your site for you, and not actively invested in what you are doing, it just means that your site will not keep up with you competitors in terms of website page speed, and your website can get penalised by search engines like google for not performing well for the end user.

The worst cost saving method we have seen from big name web hosts is to either not have any, or very limited website / hosting server backups. Sadly this is commonplace for the cheapest of the web hosts, with them claiming that its your website, so you should have a backup of it. This is very hard to do with e-commerce or similar sites that update regularly, and may have client submitted information that needs backed up. The last thing you want if your website gets infected, or if the hosting provider has a meltdown (certainly has happened in the past, even in fairly recent history from big name hosting providers) and loses your website, not being able to restore it to a known good working backup.

What we do at Webmad is a little different to many of the web hosting companies out there, and we stand by what we do.

Firstly, we run cloud based servers. What does that mean? Well – it means that our infrastructure is based on hardware provided by large internationally renowned datacenter providers, on proven systems that either self heal, or instantly move our hosting servers onto hardware that isn’t in a failed state. Downtime is minimised to only what is absolutely necessary to deliver you the best experience (ie install of software and security updates etc), and we are always on the latest and greatest hardware.

We also take backups of your website, and our entire servers, every 12 hours. Not enough? We can increase that to every 15 minutes if you need – a complete snapshot of your hosting environment – server specs, database state, all that fun stuff. And we keep that info for ages too (2 weeks for high definition backups, moving to nightly for 3 months, then monthly etc etc), so if you need to audit anything, or need as little loss as possible if something were to go pear shaped, we’ve got you covered.

Webmad have a number of shared hosting servers that our clients websites are based apon, all under the same levels of protection and running high spec hardware. We limit the number and type of sites any one server can host, so that our servers have the greatest possible uptime and greatest protection against high usage spikes impacting on other users. We run hosting and monitoring software that ensures your sites are online all the time, and if there are any issues, we can react fast to rectify the situation.

And if the worst was to happen and members of our team were taken out by a bus (or however you creatively want to dispatch of us – we don’t encourage it though), there are at least 5 of the team who can keep the lights on and your hosting safe. And our systems are set up in such a way that external contractors could also be brought in to maintain status quo as needed, so we have redundancy at all levels.

That’s all well and good, and I’m sure that others in the web hosting game can replicate this. But what really sets us apart, and we are most proud of, is that we are a local team, based in Christchurch, and we’ve been doing this as Webmad for over 10 years (some in the team, for more than 20 years). You can walk in off the street, and say hi or grab a coffee with us. Ask us all the curly questions in person, or over the phone. We are accountable. We are a team that wants to partner with you and make your endeavours as successful as we can. We celebrate our clients successes, and respond as needed if they have emergencies we can help with. We aren’t afraid to answer the phone after hours. And we’d love to be working with you, too.

Categories
Community

Websites Making A Difference

Webmad got its name because we wanted to be a part of making change in this world. Websites Making A Difference. As part of fulfilling that vision every now and then a good cause comes up where we can offer our services to help the community

One such cause came up recently. Our local community is currently getting a new public pool – the South West Leisure Centre. This is all rather exciting for the community, as we lost a great resource many years ago when the Sockburn pool was closed down. When the pool was being planned, submissions for features were put out, and one of those features which just didn’t make the cut in terms of funding available from the local council was for a hydrotherapy pool to be added into the complex

What is a hydrotherapy pool? Well its a heated pool commonly used as part of physical rehabilitation or therapy to enable weightless movement of a joint. It is useful for lots of things from arthritis relief to recovery from injury. Having the ability for local residents to benefit from this feels like a great thing to assist with.

When the local rotary club came to us with their plans to fundraise to help ensure this great facility is added into the new pool complex, we jumped on board. and that is where https://hornbyhydrotherapy.nz has come about. There is a goal to get to $1.4m funding to make this happen, and as of writing this the team are at $301k so making good strides into the funding journey.

The website is purely a front to the fundraising operation – it has been designed to be visually appealing, have all the information you need to get on board, and links off to the main online giving platform, givealittle. Built using WordPress, the Hornby Rotary team can update the site as needed along the fundraising journey, and it provides a centralised point to direct people to.

We are proud of our association with this cause, as one of the many things we are looking to do in our community to give back, and help make it a better place. If you feel like you’d be keen to help, let us know.

Categories
Development

Too many options!

Ran into a peach of an issue on friday – client complains of a report being ‘glitchy’. They have a learning management system which contains a report with a filter that lists all student ID’s in an HTML select element. No problems you’d think… until you realise there are 13,000 plus students, all listed out as options within the select element… and the page has performance issues trying to load all the options.

What can we do?

So my first instinct was to throw some javascript at it, and convert the problem from being a select element to being a div with some javascript to handle displaying a much smaller subset of options depending on what is being typed – Select2 is my go-to javascript select replacement library, so we threw that at it.

Did it work? No. Same performance issues, but they were less as you filtered down the result set by entering digits… So its a bit of a better look, but it still ain’t right. What a pickle! Where to now?

After a period of trawling Google search results for a solution, I’ve stumbled upon the datalist html element. There is talk of it being a more efficient option as a select alternative… so here is what I’ve done:


jQuery('#id_filter_fuserfield_idnumber').after('<input type="text" list="filt_students" id="id_filter_fuserfield_idnumber_entry"/><datalist id="filt_students"></datalist>');
var opts = "";
jQuery('#id_filter_fuserfield_idnumber option').each(function(k,v){ 
    opts += "<option "+jQuery(v).attr("selected")+">"+jQuery(v).text()+"</option>"; 
	if(jQuery(v).attr("selected")){
		jQuery('#id_filter_fuserfield_idnumber_entry').val(jQuery(v).text()); 
	});
}
jQuery('#filt_students').append(opts);
jQuery('#id_filter_fuserfield_idnumber').hide();
jQuery('#id_filter_fuserfield_idnumber_entry').on('change',function(){
	jQuery('#id_filter_fuserfield_idnumber').val(jQuery('#id_filter_fuserfield_idnumber option:contains("'+jQuery('#id_filter_fuserfield_idnumber_entry').val()+'")').attr('value'))
});

So to explain this:
– add text input and link empty datalist after the select element (note no name on the text input so data not submitted with form).
– populate the datalist with items from the select element. If an item from the select options is marked as selected, update the text box to reflect that.
– hide the original select element.
– listen to changes on the text input so that when a value is chosen, the select has its value updated to match the chosen value.

Testing this, it is really fast. Like – really fast. No performance issues with 13,000 options to chose from, and all behaves as expected very similar to a select inpout, but you have the advantage of being able to use the text input to start typing and filter the list of elements to chose from accordingly. Vary cool!

In summary – don’t always reach for Select2 to solve select problems – the datalist element is your friend, and offers similar basic functionality (yeah I know – select2 can do a bunch more esp when it comes to ajax loading etc, so horses for courses, but if you don’t need the extra functinality…). I know I’ll be looking at using datalists more going forward.

Categories
Hosting Security

Vulnerability

Being vulnerable is powerful starting point for learning and change. When it comes to software, this is also the case, but never in a good way or at a convenient time. This past week we have been notified of a relatively serious vulnerability in the WordPress website content management system. In this post we will explore the issue, the resolution, and actions we can take to ensure exposure is minimised.

So mid afternoon NZ time on the 7th of Jan, 2022, we were alerted to a new wordpress security vulnerability – https://vuldb.com/?id.189817. The vulnerability report is kinda bland but here is a more detailed explanation.

What researchers found, was that an authenticated wordpress user with the ability to manage tags, or categories, or content metadata (attributes associated with content) could manipulate the data so that additional commands could be sent to the database server. So for example (and this is crude and untested), someone could fashion a request that contained an ‘IN’ component containing “‘; truncate table wp_users;”, and you would find that you’d lose all the content from your wordpress users table, and that is kinda unhelpful.

Once this vulnerability was found, the wordpress development team have been working on how to patch this to prevent issues. The patch has been published at https://github.com/WordPress/wordpress-develop/commit/c09ccfbc547d75b392dbccc1ef0b4442ccd3c957 but to explain what they are doing, basically they are replacing any space characters with underscores in the inputted data, so it all looks like one word, and an sql statement cannot be made.

So how serious is this vulnerability? Well it depends how much you trust your users, and how much access you give them to curate their own datasets. So for your average wordpress site that is just a brochure site, no user logins etc, there is minimal risk, as you are curating the content for the end user, therefor the requests will be safe as you won’t want to scupper your own site. But giving users the power to enter or alter data, well that’s where it can all go wrong if such capability is in the wrong hands, and if exploited, could mean very serious implications for your database.

For all of Webmad‘s hosted wordpress site clients, we have patched this vulnerability on all potentially effected sites on our managed servers, eliminating the risk here, but if you have a website you think could be at risk, certainly get in contact and we can patch / update your site too.

As per other posts on this site, the key is to keep your website software updated to the latest versions, so that any security issues are found and repaired as soon as possible to reduce vulnerability. Much of this either requires keeping up to date with the current threats by following threat boards etc, or ensuring you have a regular update schedule for your site. With wordpress you can also turn on auto updating of websites, which helps automate the ‘keeping on top of things’.

Categories
Hosting Security

Log4j and global panic

Now-a-days, the world is getting used to things being thrown at it to worry about. And we all hope that smart cookies in a lab somewhere will find a cure. Well – a couple of days ago, some boffins found a new computer bug that is being given hazard level 10, and I can assure you – that gets us geeks all rather excited

CVE-2021-44228, or the Log4j bug, was first published, with a patch, on the 9th / 10th of December. This vulnerability, which was discovered by Chen Zhaojun of Alibaba Cloud Security Team, impacts Apache Log4j.

Yip – that’s all foreign language to most humans, but the long and short of it is, this is a fresh vulnerability found in a piece of software very commonly used across the world for storing software activity logs, that allows anyone without permission, access to hijack a computer system and effectively run their own commands – from establishing a ransomware attack on a host, through to compromising secure user records etc.

The vulnerability has been shown to be active in software that uses the log4j software as well – from well known names like Apple iOS (yep – your mobile phone / tablet), MacOS, VMWare, Discord, Ubiquiti etc – A list is starting to be collected via https://github.com/YfryTchsGD/Log4jAttackSurface – a patch has been released to counter the attack, but the slower people are applying the patch, the more exposed systems are, and the more havoc that can be applied globally.

So what can we do?

  • Check for, and apply, any updates from software manufacturers. Always make sure you are running the latest versions of everything. This is paramount for both your security and your piece of mind.
  • Consider application of a strong, secure firewall to block potential threat traffic from getting to your systems
  • Contact any providers you use that could be storing sensitive information and seek assurances that they have taken appropriate measures to counter the risk associated with this new threat

Here at Webmad all of our hosting systems have been secured against this threat, simply because we are not using any services that rely on Log4j, and any of our upstream providers have been quick off the mark to get this resolved. Should you have any concerns though, by all means get in contact.

Categories
Hosting Security

Never trust an email

Over the last week, some of our shared hosting clients have been targeted by a rather complex email attack that is focusing on clients using cPanel based hosting, like we use at Webmad.

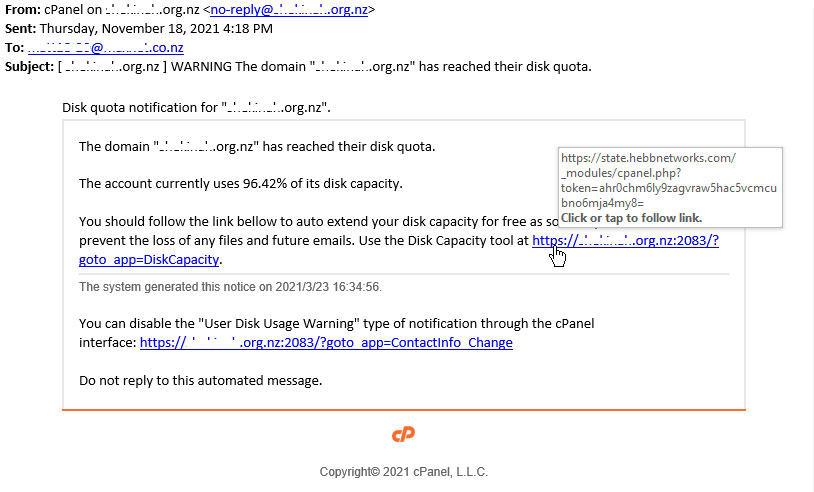
The attack first detects if the website hosting is cPanel based, and then if it can locate a contact email address form the website, it emails the contact with an email that looks like a legitimate cPanel disk space usage warning email, requesting you take various actions to protect your website from downtime.

This typically looks like the following:

So the key components of the email to look out for are:

  • If you hover your mouse over the links in the email, they are not the same as the link text. This is a huge red flag, as it is misleading you as to where you think you are being directed.
  • The From address always has ‘no-reply@’ at the start – most hosting providers will customise this so it comes from them, not from your own domain name
  • The disk usage percentage is always over 95%

Please ignore these emails, and if you have followed any of the links, do let your hosting provider know as soon as possible, as it is possible that details you provide on the links will lead to compromising your websites hosting security – its best to work through with your hosting provider the best course of action from here.

For Webmad hosted clients – we don’t actually have set disk quotas on our hosting, so we can assure you you will never receive any legitimate emails like this from us – we prefer to contact you directly, using humans not automation. Contact us if you ever have any concerns.

Stay safe out there everyone!

Categories
Hosting Technology

Aaargh! Facebook is down!

What a shock to many – their worlds coming crashing down as the need for social interaction is unable to be met by the worlds most commonly used social networks, all owned by Facebook. Today (5 Oct 2021) – many here in New Zealand have woken to a worldwide outage, visiting the site is complaining about a DNS / Domain issue, and a white screen that no doubt has some rather high paid network engineers at Facebook, having kittens.

So why is it down? Well – that’s the question everyone is speculating on, and much of it comes down to the core structure of the internet, and how they are harnessing tools to give us all the best experience possible. The most likely reason is what I’ll be walking us through today.

How does the internet work?

Well it all starts off in your internet browser – Google Chrome, Mozilla Firefox, Internet explorer / Edge / whatever Microsoft are calling it now, Apple Safari. Lots of options, all work the same way. You type in a web address (URL) into the address bar, and hit enter, and within seconds the page you want renders in the browser, and we carry on our merry way. But there is a bunch of communications that goes on within those few seconds that helps make this all work.

The first part of this is the address translation. There is a global system called DNS (the Domain Name System) which translates what you have typed in (ie https://webdeveloper.nz/ ) into a series of numbers called an IP address. The servers that store the website data each have an IP address that they respond on, and deliver the web pages back to you. Its a bit like your phonebook. I want to call someone by this name, so please give me their phone number to do so.

Once the address translation has happened, you can talk directly to the servers and get the data you need to render the web page. The faster this translation happens, the faster your website will load for the end users. And this is where the problem is believed to have happened for facebook today.

Where has it all gone wrong?

The way that normal IP addressing works is that one server typically has one IP address. It is unique, and you can get a bunch of details from it (check out https://ip-api.com for some of this info). The downside is that a single IP address typically translates to one server, that may actually be on the other side of the world to you. And because light can only travel so fast (ie the internet backbones that link us all together via fibre optic cables) there is a delay talking from little old NZ through to big datacenters in the USA or Europe.

What some clever clogs has worked out though, is that you can use Content Delivery Networks to reduce the physical distance between your web servers and your customers around the world, making websites load so much quicker. Yay! But that is only part of the equation. This works for website content, but it doesn’t work for the DNS lookup / translation aspect. And this is where we get to BGP routing. This is where we believe the outage has been caused today.

You’re getting technical…

BGP Routing or Border Gateway Protocol Routing, is a fancy way of allowing one single advertised IP address to be shared by multiple servers globally, which can then serve website clients from the closest possible geographic location. As there are lots of servers that can serve the data of the one IP address, it can be very fault tolerant, and increases speeds of users getting website addresses translated to IP addresses so that the traffic can be routed to the right places and the websites work

In todays outage, the hardware that does this BGP routing globally for Facebook, allowing them high website speeds, has been misconfigured / lost its configuration. What this has meant is that anyone trying to do lookups / translations of any of the facebook operated web addresses, are getting blank screens with their browsers telling them that they can’t find the domain name.

As I write this it looks like things are slowly starting to resume normal operations after 4 and a bit hours – there is a facebook branded error page now, so we are at least seeing facebook servers again, but I suspect the next issue they will face as they slowly bring the site back online is the large influx of people accessing the sites after their drought, and trying to catch up, effectively swamping their servers

What can we learn from this?

  • Firstly – in the internet world, you are never to big to fail.
  • Secondly – the world is still ok without social networks.
  • All the geekery in the world (CDN’s, BGP Routing etc etc) won’t necessarily save you from good old fashioned human error, although it does help reduce its occurance.

Here at Webmad we are well versed in using these various tools to get you the best outcomes and speed for your website, using trusted providers, and offering proven results. We’ve run sites using BGP failover routing to offer high availability geolocation aware systems within NZ, we use CDN‘s all the time, and we can quickly pinpoint where issues might be, and how to fix them. Could we fix Facebook’s troubles? That’s a bit above our pay grade, but we can definitely put our knowledge to great use as part of your web team. Drop us a line to get the best results for your online assets.

Categories
Interaction Security Technology

Cookies – trick or treat?

One of many annoyances of the internet these days is the dreaded ‘Please accept our cookies’ popup you see on a great number of websites, warning you of the intention of the site you are visiting to give you things called cookies. They sound soo sweet, digestable, and innocent. But how many of us actually know what they are, how they are used, and if they are dangerous or not?

So – what is a cookie and why are they on the internet?

A cookie, in the internet sense, is a wee fragment of data that a website can store in your web browser for a defined period of time. This can be until you close your browser, it can be days or weeks. Once a cookie is stored on the end users browser, that cookie of information is sent to the server with every new page request or interaction with that websites server. Cookies are restricted to only send data back to the domain name that set them. A cookie is unique to each user – they may store the same information, but because they are stored on the end users device, they are unique to that user.

Where they get powerful is that website developers can store data in a cookie that enables them to customise our browsing experience on their website. Typically what this looks like is when a user has logged in to a website a token is stored on a cookie for that user session so that every subsequent request to the server can prove that it is from the logged in user, and the server can customise its response according to your profile and stored settings. This is really useful.

Where this can get risky though, is when you visit websites that use advertising networks. Advertising networks can set cookies on your computer to track what websites you have visited, and your preferences so they can target you with ads for things they think you need. This is seen as predatory, and can give these networks a huge wealth of information about you and your online habits. The more websites an advertising network is used on, the more data they can collect.

Its this predatory use of cookies on websites that has given cookies their bad name. Cookies as an object are quite harmless – they do not contain code that gets executed or anything dangerous, but they can store information that can be used to identify individual users and ‘follow’ them around. To break up the amount of data that can be used to identify a user, it is recommended to either use a cookie blocker in your browser that can determine if the cookie is from an advertising network or not.

While cookies are generally safe to accept, websites in many geographic locations nowadays need to request the users permission before they can store cookies in their website browsers. The lawmakers in these regions pass laws to make this mandatory for sites doing business in these regions so that their people can make informed decisions on what information can follow them around on the internet.

If you visit a website that you know you won’t be logging in to or signing up for, then there is no need to accept the cookies on that site. If you are keen to interact with the site, and have a customised experience, then accepting cookies is quite fine. You can always clear out cookies from your browser at any stage – the process varies depending on what web browser you are using, but you can view the content of any of the cookies, and delete whichever ones you prefer.